A wallet that
follows only you.
Self-custody for Tari Ootle. Sapient generates and holds its own 24-word recovery phrase, then signs and submits transactions straight to the network. No wallet daemon required.
Everything a self-custody wallet should be
Built directly against the Ootle network. No guessed balances, no re-pasted addresses, no daemon to babysit.
True self-custody
Generates and holds its own 24-word recovery phrase. Keys are derived and used on-device, and they never leave the extension.
No daemon required
Signs and submits transactions directly to the network. Optionally connect a running tari_ootle_walletd for hardware-wallet-style external accounts.
window.tari provider
A MetaMask-style injected provider for dApps: connect, sign, and submit in the page's own context, not a WalletConnect relay.
Multi-account
Multiple accounts per wallet, each independently derived. Switch freely without re-entering your seed.
Address book
Save recipients once, pick them from a list on Send or Send-privately. No more re-pasting long addresses.
Network switching
Move between Esmeralda and Igor testnets from Settings, with a confirmation step so you never sign on the wrong one by accident.
Transaction history
Every send, shield, unshield, private transfer, and dApp transaction recorded locally, labeled clearly without ever decoding raw instruction data.
Real on-chain balances
Every token renders with its actual on-chain divisibility and symbol, read from the network, never a guessed constant.
Testnet faucet built in
Claim testnet XTR straight from the home screen, including the self-funding path a brand-new, empty account needs for its very first transaction.
The part most wallets bolt on later, shipped from day one
A connected site sees only what you explicitly grant, never your full position by default.
Stealth-type transfers
Shield, unshield, and send-privately. The wallet builds every stealth output itself, coin selection included; a dApp only ever supplies an amount, never a blinding mask or view secret.
View-key-gated confidential balances
Reading your private position is a separate, revocable grant from connecting. A site can know your address without ever learning what you actually hold.
Private transaction fees
The fee itself can be paid from a stealth UTXO instead of your visible balance, so the transaction doesn't reveal an active account on-chain at all.
Encrypted memos
Attach a private note to a stealth output, visible only to its recipient and never recorded in the clear on-chain.
Native HTLC support
Fund, claim, and refund hash-time-locked contracts directly, the primitive cross-chain swaps and trustless escrows are built on.
Reveal straight into a dApp call
tari_withdrawStealthAndExecute pulls stealth funds directly into a caller's own contract call in one signed transaction, with no separate reveal-then-send round trip.
Checked, not just claimed
Two rounds of internal, code-level self-audit: different passes, different tooling, both publicly documented rather than kept private.
Real bugs found, fixed, and written up
An auto-lock bypass, a scan cursor that could permanently skip a private payment, and storage races between concurrent requests: every one documented with file/line references in SECURITY_AUDIT.md, not smoothed over.
AES-256-GCM at rest, 600k-iteration PBKDF2
Meets OWASP's 2023 minimum. The decrypted seed lives only in chrome.storage.session, never reachable from a content script.
Mandatory seed verification
Create Wallet gates past the recovery-phrase screen with a spot-check (re-enter three random words) before finishing. No more trusting an unverified "I saved it" click.
MIT licensed, fully open source
No noncommercial clause, nothing closed off. Read every line the seed and signing logic actually run, on GitHub.
Real dApps, already running against it
A MetaMask-style window.tari provider: connect, sign, and submit in the page's own context. Not a relay, not a bridge.
A full DEX
Token creation, liquidity-pool creation, adding liquidity, and swaps, including the multi-instruction, multi-retry transactions those flows require, exercised live end-to-end.
A sealed-bid DAO
Reveal → deposit → withdraw-confidential → place-bid, chained through tari_withdrawStealthAndExecute as one wallet-signed transaction, verified against a real bid with no dry run.
Your dApp next
The full provider API (transaction requests, private-balance access, stealth sends) is documented and ready to build against today.
universe.tari.mw/integration
See it in action
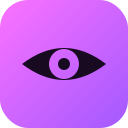
The full flow (balances, sending, and dApp approvals) in a compact popup that stays out of your way.
 Sapient
Balances at a glance
Real on-chain divisibility and symbol for every token you hold.
Sapient
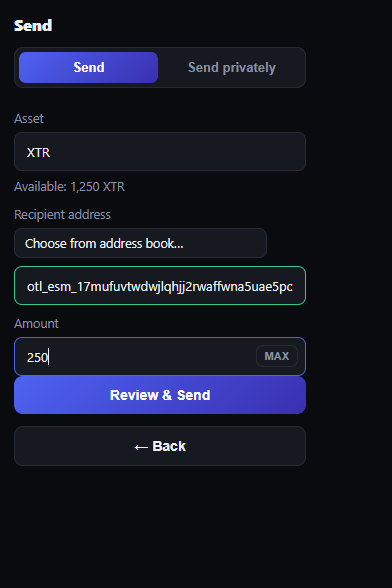
Send to a wallet address
Just paste an otl_… address. Sapient handles the rest, even for brand-new recipients.
Sapient
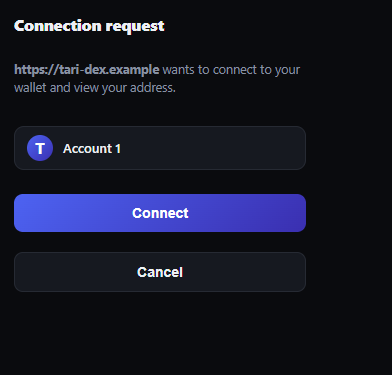
Explicit dApp approval
Every connection, sign, and view-access request is a clear, reviewable popup.
From seed to submitted transaction
Create or import
Generate a fresh 24-word recovery phrase, or import an existing one. A password locks the extension between sessions.
Derive & hold keys
Account keys are derived on-device. Sapient signs with them locally, and the seed never leaves the extension.
Build & approve
A dApp requests a connection or a transaction; you review and approve it in a dedicated popup, every time.
Submit directly
The signed transaction goes straight to an Ootle indexer. No intermediary daemon required for your own accounts.
Money was always a bearer instrument. Here's why we think it should stay that way.
Why privacy and programmability had to end up in the same primitive, and why that's specifically what led to building Sapient on Ootle, not just another privacy chain. Read the essay →
Why "Sapient"?
Named after sapient pearwood, the self-aware wood Discworld's ever-loyal, fiercely protective Luggage is carved from. Fitting for a wallet that follows only you and answers to no one else, in the same nerdy-but-earnest naming tradition as Tari's own testnets (Weatherwax, Igor, Esmeralda, all Discworld references too).
Own your keys on Ootle.
Free, open-source, and built for testnet experimentation today.
We don't sell your data. We don't take a cut of your fees.
Sapient exists to make Ootle usable, not to extract revenue from the people using it. Read the full reasoning behind that.
There's no business model here. No analytics, no data broker, no premium tier, no markup baked into a fee. Sapient is built by people who take the Cypherpunk's Manifesto at its word: someone has to write the software, so we're writing it, and we're not going to fund it in a way that quietly undoes the point. The only thing keeping this maintained is direct support from people who want Ootle and the dApps built on it to keep existing.
12Gtjb5qbgYBbF9meZ31HKnEusGgnwfbDYBcZV3k4xko1htBQisjvgMW1zJL4gERkcryLntDKLqK2GQ2xEKD2i6Bq8s
This is an L1 (Minotari) address, not an Ootle otl_esm… address. Sending Ootle-native tokens here will not work.